
AgentDish directory
security
Accepted listings with this tag.
| Listing | Category | Score | Trend | Checked | |
|---|---|---|---|---|---|
#12
↑ +16
Snyk Agent Scan
Open-source security scanner for AI agents, MCP servers, and agent skills. It auto-discovers installed agent components and checks them for prompt injection, tool poisoning, secrets, malware payloads, and related risks. |
Security / Agent Security | 92 | ↑ +16 | 164 days ago | Details |
#14
↓ -3
Vigil
An AI harness for long-running penetration tests, bug bounties, and code audits. It combines specialist agents, a Kali runtime, durable state, and second-agent verification for findings. |
Security / Penetration Testing | 91 | ↓ -3 | 6 days ago | Details |
#33
↓ -2
Would You Merge It?
An open-source code-review training repo with 24 AI-written bug katas in Python and JavaScript. It includes runnable tests, fix-and-verify workflows, and GitHub Actions grading for forks. |
Developer Tools / Testing & Code Review | 90 | ↓ -2 | just now | Details |
#60
↓ -2
Molt
Molt is an open protocol for letting an AI agent make bounded purchases through disposable, single-use payment credentials. The repo includes a clear quickstart, MCP integration, a threat model, and a working test-mode demo. |
Developer Tool / AI Agent Infrastructure | 90 | ↓ -2 | 63 days ago | Details |
#64
↓ -2
BoundaryBench
BoundaryBench is an open-source benchmark for coding agents running under hardened sandbox policies. It compares harnesses like Claude Code, Codex, Terminus 2, and Grok on Terminal-Bench tasks and includes quickstart, policy controls, and result export tools. |
Developer Tools / Code Assistant | 90 | ↓ -2 | 72 days ago | Details |
#66
↓ -2
Agentmetry
Open-source, local-first audit trail and detection layer for AI coding agents. It records tool calls from Cursor, Claude Code, Codex, and MCP servers, adds MITRE ATT&CK tags, correlates risky sequences, and can forward events to SIEM tools like Loki, Elastic, and Splunk. |
Developer Tools / Code Assistant | 90 | ↓ -2 | 76 days ago | Details |
#189
→ 0
TakoVM
Open-source sandboxing and secure file system for agent code execution, with built-in job queues, execution history, retries, Docker isolation, and optional gVisor hardening. |
Developer Tools / Agent Infrastructure | 89 | → 0 | 108 days ago | Details |
#198
→ 0
Bright Security Agent
GitHub Marketplace app from NeuraLegion that scans apps and APIs for vulnerabilities, proposes fixes, and validates remediations inside GitHub workflows. |
Security / Application Security | 89 | → 0 | 132 days ago | Details |
#200
→ 0
Redact
Browser extension that scans pastes for credentials and PII before they reach LLM chat sites, with local on-device inference and no network calls. |
Developer Tool / Browser Extension | 89 | → 0 | 136 days ago | Details |
#244
↓ -3
BurpSqueezer
A Rust-based security research tool that converts Burp Suite XML dumps into compact Markdown reports for LLM-assisted analysis. |
Developer Tools / Code Assistant | 88 | ↓ -3 | 31 days ago | Details |
#335
↓ -3
Setoku
Open-source, self-hosted MCP knowledge server for AI agents that adds read-only access to company data, preserves business context, and can publish live dashboards as apps. |
Developer Tools / Code Assistant | 88 | ↓ -3 | 86 days ago | Details |
#348
↓ -3
clawk
Disposable, network-restricted Linux VMs for AI coding agents. The project is built for letting coding agents install packages, run tests, use system tools, and work inside an isolated machine instead of the host laptop. |
Developer Tools / AI Coding | 88 | ↓ -3 | 96 days ago | Details |
#354
↓ -3
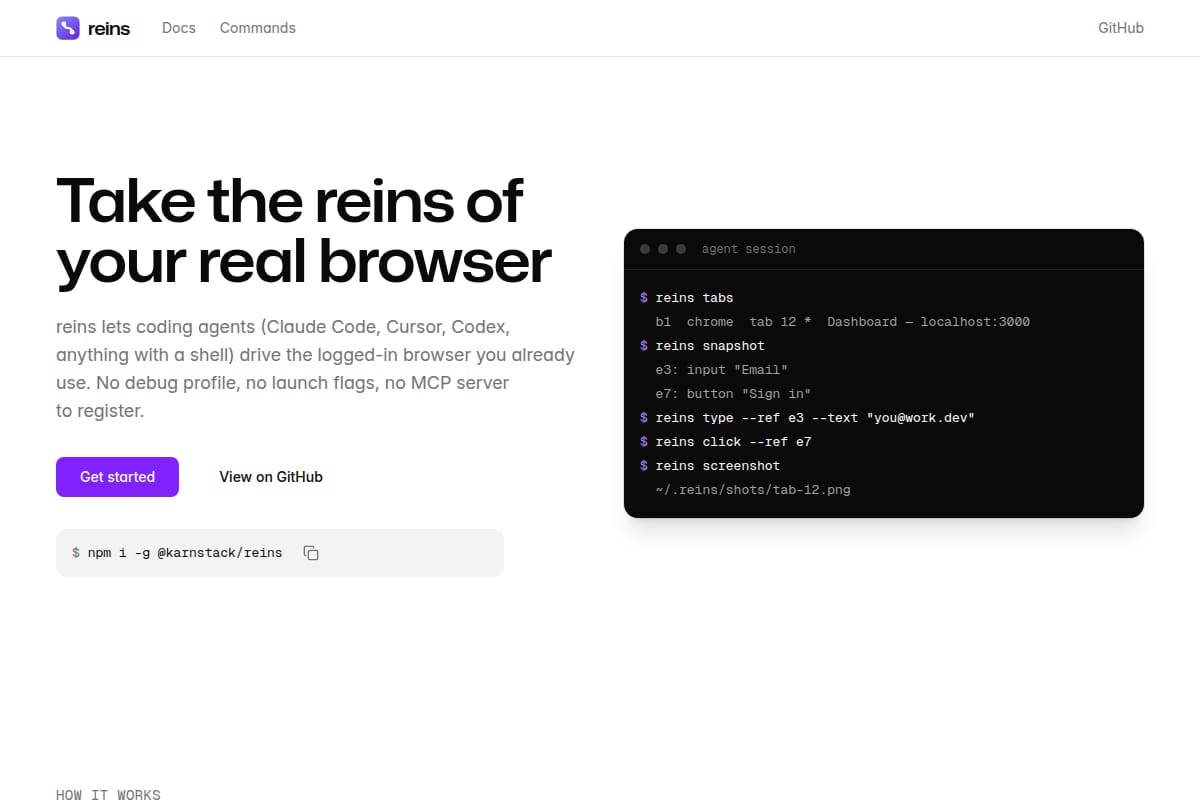
reins
Local browser-control tool that lets coding agents drive a signed-in Chromium browser through a CLI, daemon, and extension. |
Developer Tools / Code Assistant | 88 | ↓ -3 | 101 days ago | Details |
#416
↓ -3
Recursant
Open-source platform for governing AI agents across clouds and stacks, with a control plane, sidecar-based data plane, policy enforcement, observability, and audit trails. |
Developer Tools / AI Infrastructure | 88 | ↓ -3 | 163 days ago | Details |
#440
↓ -4
Spens
Spens is a developer tool for running coding agents in sandboxed Docker containers with network controls, secret handling, and detailed logs of LLM calls, tool use, and file changes. |
Developer Tools / Code Assistant | 87 | ↓ -4 | 15 days ago | Details |
#446
↓ -4
Kern Sandbox
A local sandbox for running LLM-generated code from Python or Node with no cloud, no daemon, and strong isolation controls. |
Developer Tools / Sandboxing & Security | 87 | ↓ -4 | 19 days ago | Details |
#463
↓ -4
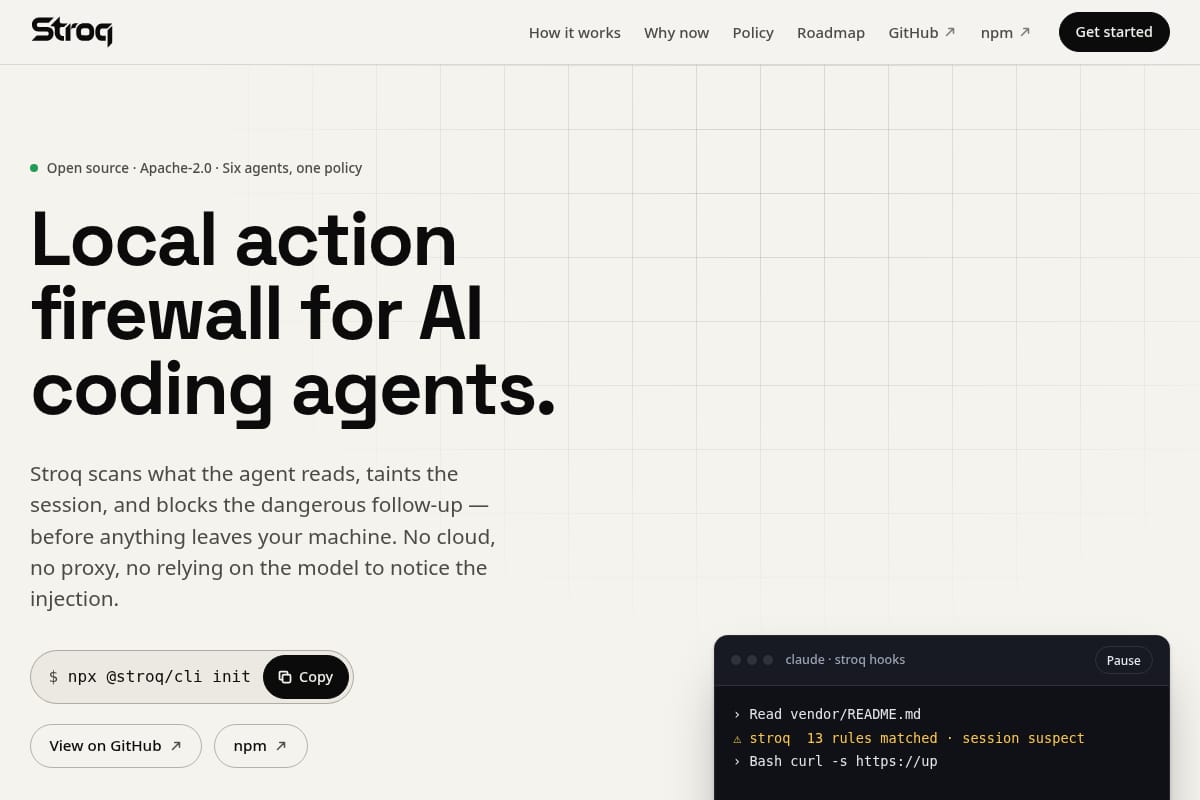
Stroq
Stroq is a local action firewall for AI coding agents. It scans tool output, marks risky sessions, blocks dangerous follow-up actions, and keeps a hash-chained audit log, with support for Claude Code, Cursor, Codex, Copilot CLI, Windsurf, OpenClaw, and MCP clients. |
Developer Tools / AI Security | 87 | ↓ -4 | 35 days ago | Details |
#489
↓ -4
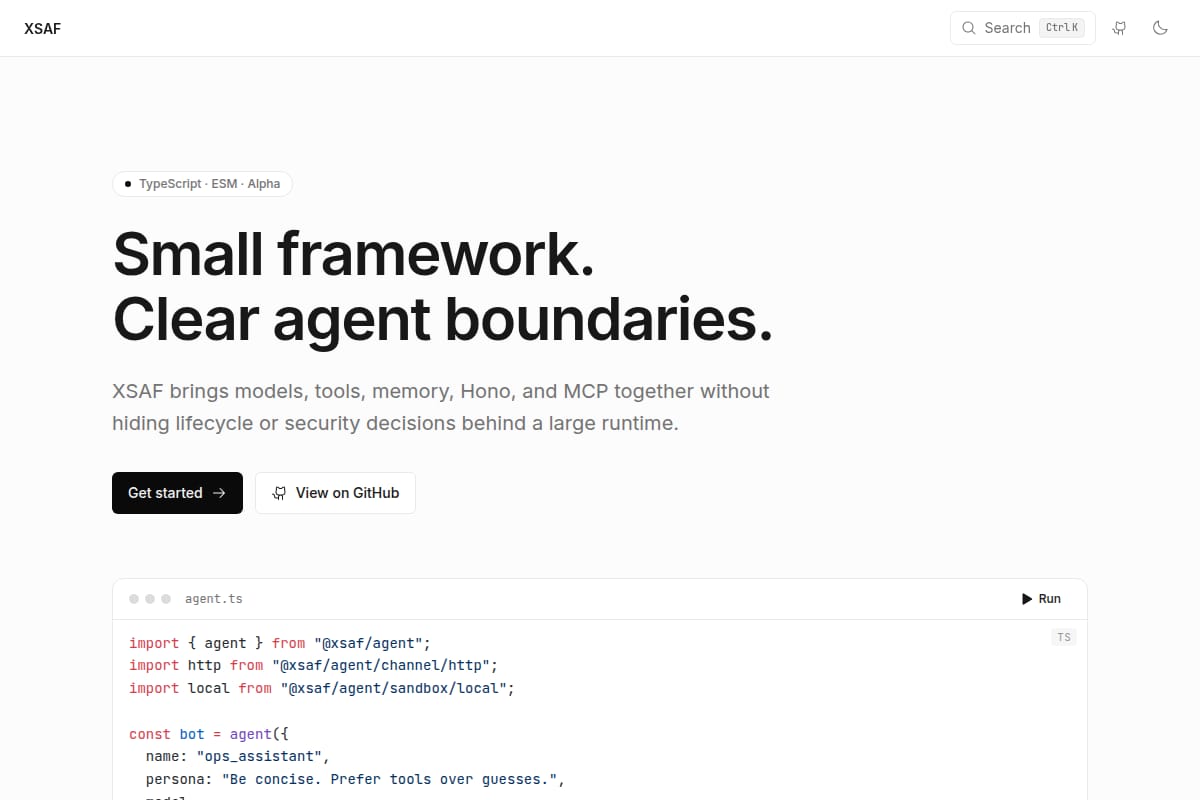
XSAF
XSAF is a small, fetch-native TypeScript framework for building secure AI agents. The page shows its core API, agent lifecycle, tool pipeline, MCP support, session handling, and offline testing story. |
Developer Tools / Code Assistant | 87 | ↓ -4 | 71 days ago | Details |
#505
↓ -4
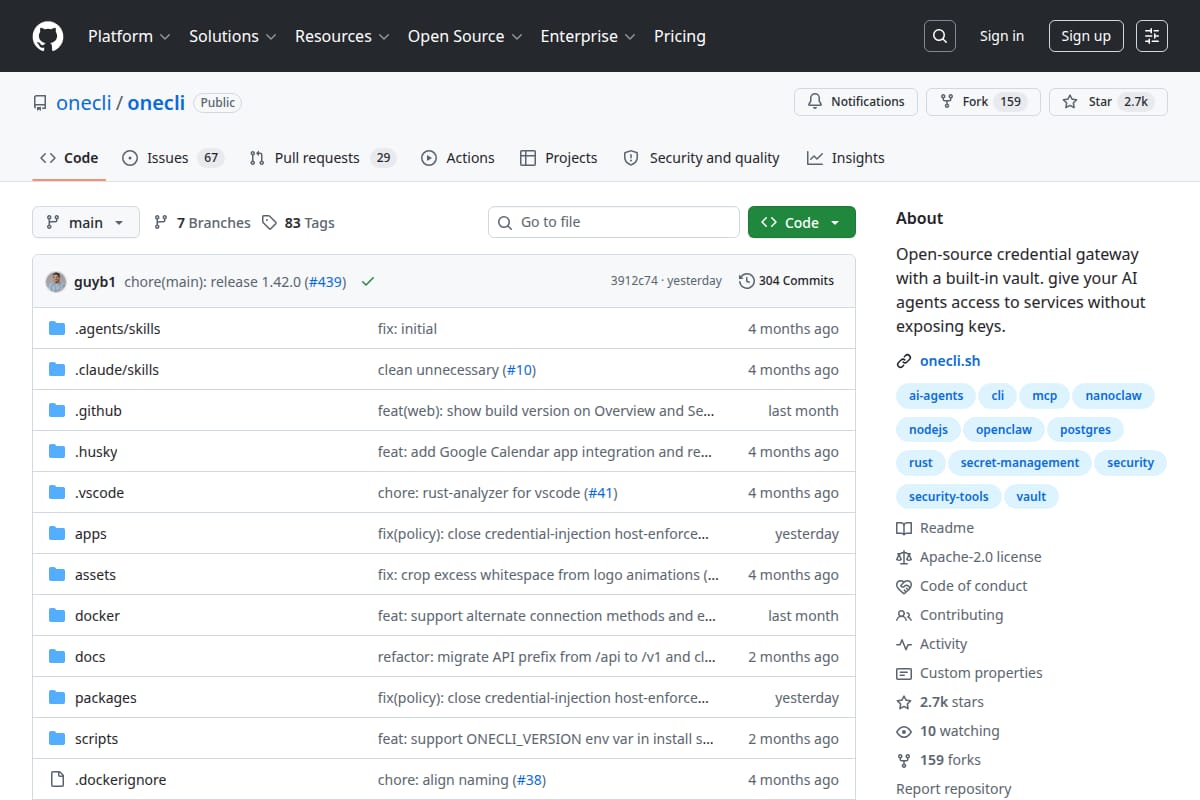
OneCLI
Open-source credential gateway for AI agents that injects service credentials without exposing the real keys to the agent. Includes a vault, access tokens, host/path matching, and local quick-start instructions. |
Security / Secrets Management | 87 | ↓ -4 | 85 days ago | Details |
#534
↓ -4
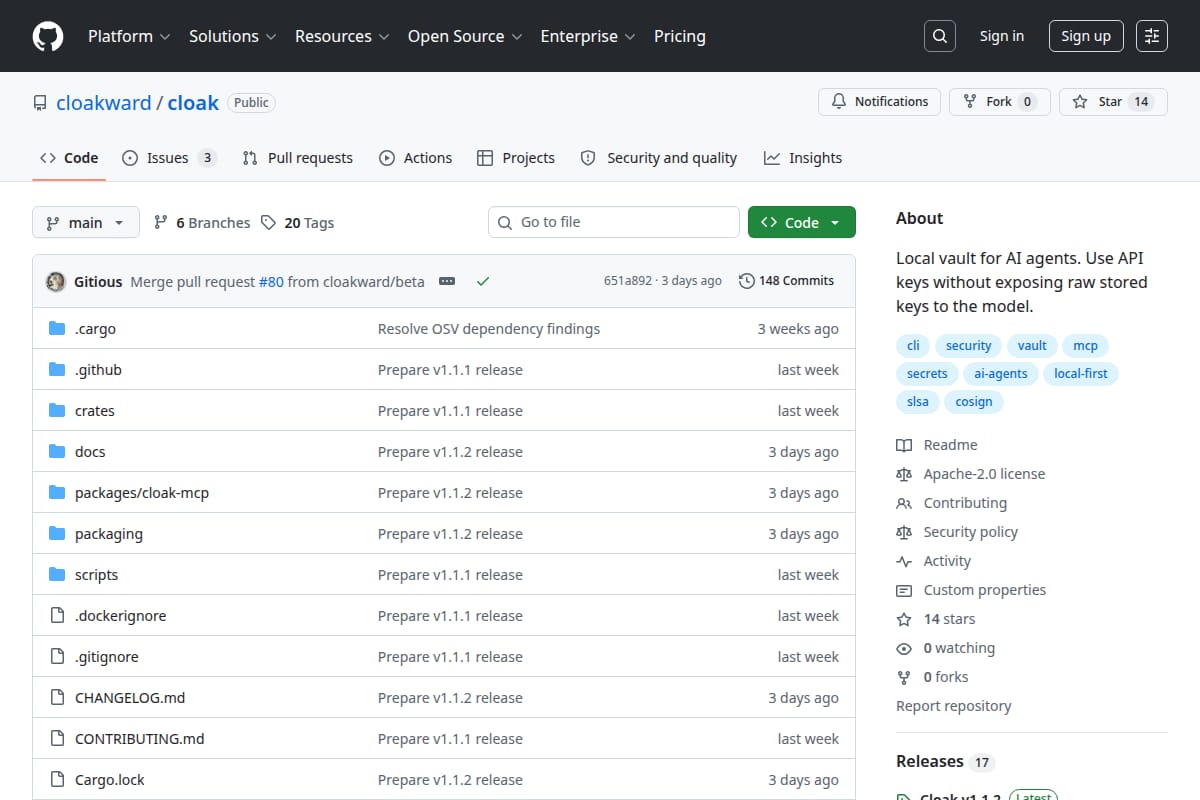
Cloak
Cloak is a local secrets vault for AI agents that lets them use API keys without exposing the raw key to the model. The repo shows a CLI, local daemon, MCP server, policy controls, and quickstart commands for connecting with AI clients. |
Developer Tools / Security / Secrets Management | 87 | ↓ -4 | 118 days ago | Details |
#570
↓ -3
Recursant
Open-source agentic mesh for governing AI agents across enterprise systems, with identity, policy enforcement, audit trails, observability, and Kubernetes-native deployment. |
Developer Tools / Code Assistant | 87 | ↓ -3 | 164 days ago | Details |
#597
↑ +2
MILLENNIUMS.AI / Redthread
AI-native application protection platform with autonomous LLM pentesting, proof-of-concept exploit findings, and a full API-driven workflow for scans, reporting, and remediation. |
Security / AI App Pentesting | 86 | ↑ +2 | 19 days ago | Details |
#604
↑ +2
agent-chaperone
An open-source tool that screens AI agent tool calls and tool results before they are used. It works as an MCP proxy plus hooks adapter, with policy-based decisions, shadow mode, and local logging. |
Developer Tools / Code Assistant | 86 | ↑ +2 | 25 days ago | Details |
#608
↑ +2
Talos
Self-hosted AI agent for terminal and Telegram with Claude/Codex workers, live activity, and a deterministic permission kernel that gates every tool call. |
AI Agents / Personal Assistants | 86 | ↑ +2 | 29 days ago | Details |