Security / AI Security Research

AI Hack Watch

A public timeline and dataset of notable AI-involved hacking and cyber incidents, with RSS support and source links for each entry.

Clear27/30
Useful25/30
Specific16/20
Complete14/20
AI Hack Watch screenshot

Why it was accepted

The page is clearly an AI-adjacent product with a concrete purpose: tracking and cataloging notable incidents where AI materially participates in hacking, exploitation, or cyber operations. It provides enough evidence for a useful public listing, including a methodology section, a visible incident timeline, source/archived links, and RSS support.
Weakness

The snapshot shows the timeline and definitions, but not the full dataset shape, available export formats, update cadence, or whether the JSON/RSS feed includes searchable fields and historical coverage.

Review status

25 days ago #1566 ↓ -2

Last evaluated 25 days ago. Current rank #1566. Down 2 spots in the rankings.

Score history

82

Related listings

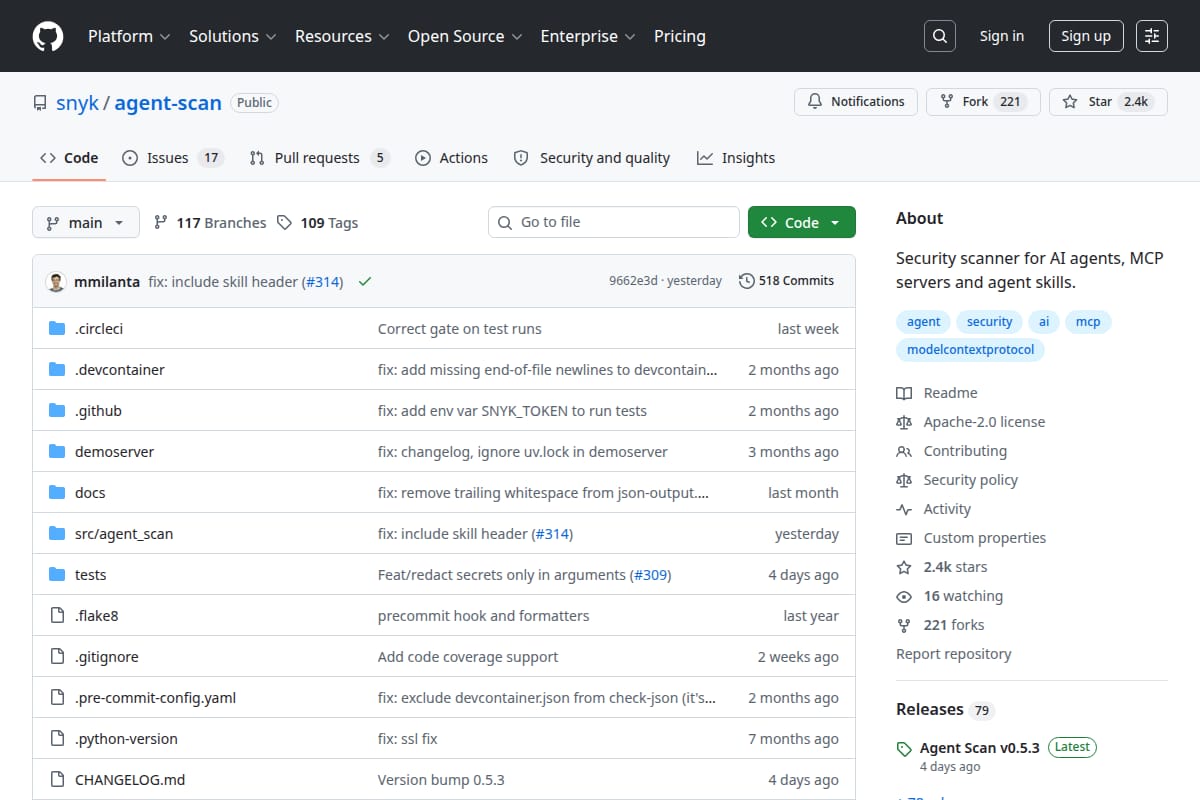
Snyk Agent Scan screenshot

Security / Agent Security

Open-source security scanner for AI agents, MCP servers, and agent skills. It auto-discovers installed agent components and checks them for prompt injection, tool poisoning, secrets, malware payloads, and related risks.

Vigil screenshot
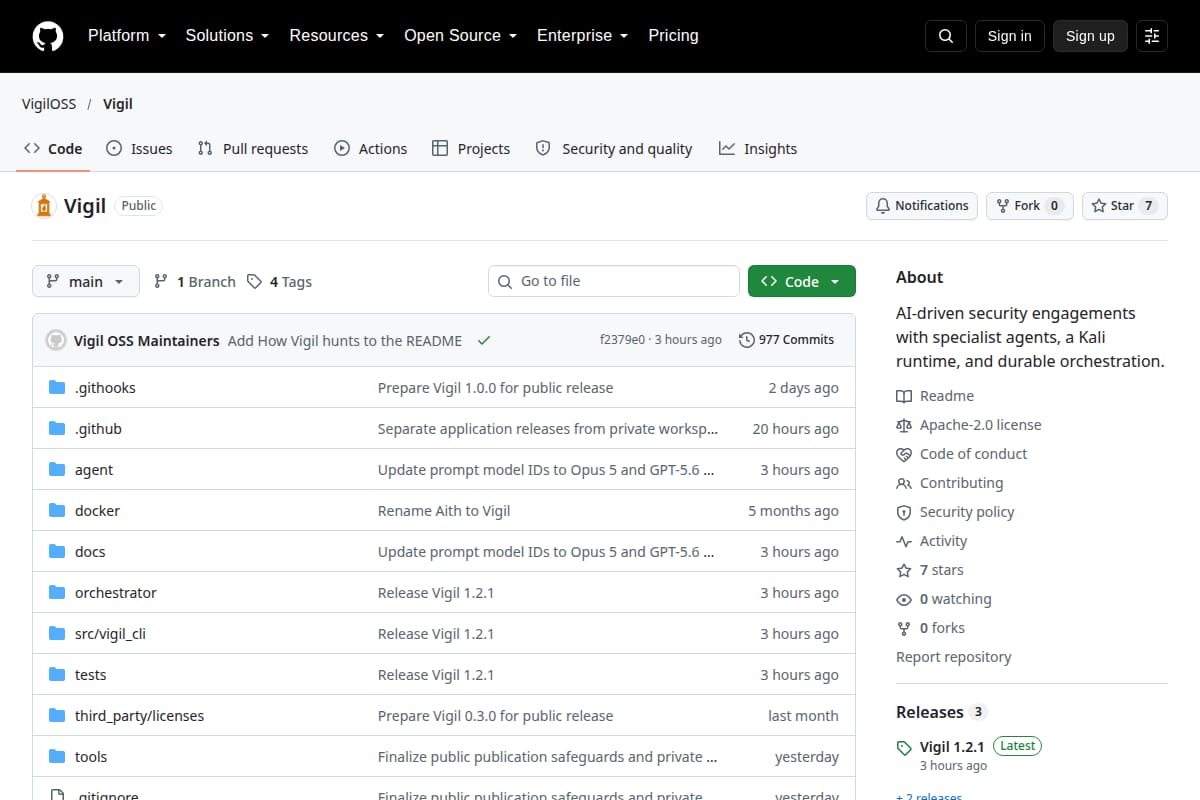
#14 Vigil
91

Security / Penetration Testing

An AI harness for long-running penetration tests, bug bounties, and code audits. It combines specialist agents, a Kali runtime, durable state, and second-agent verification for findings.

Cynative screenshot
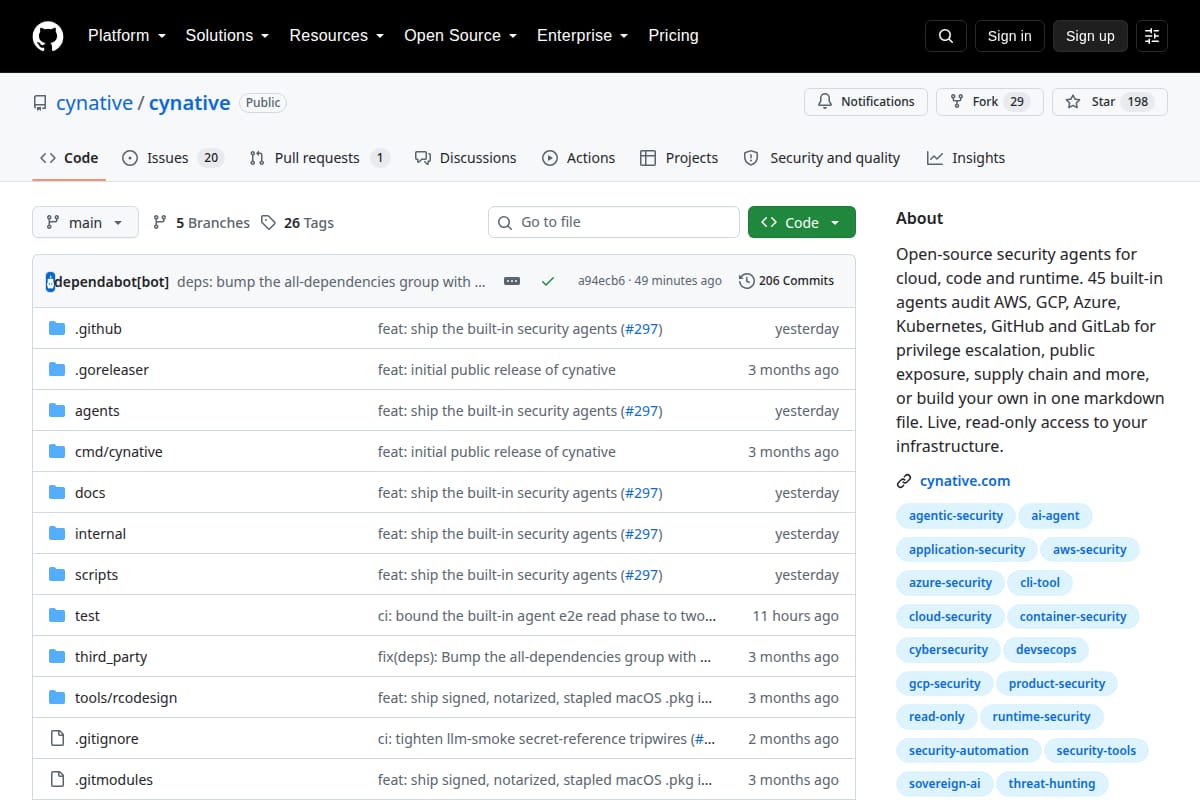
#16 Cynative
91

Security / Cloud Security

Open-source security agent framework for cloud, code, and runtime. It ships 45 built-in agents for AWS, GCP, Azure, Kubernetes, GitHub, and GitLab, and lets users create custom agents in a single markdown file.

Xalgorix screenshot
#75 Xalgorix
90

Security / Penetration Testing

Self-hosted AI security testing platform for authorized pentesting and bug bounty workflows, with a local web UI, live agent telemetry, verified findings, and branded PDF reports.