Security / Vulnerability Tracking

Anthropic Credited CVEs

A GitHub repository tracking vulnerabilities credited to the Anthropic research team, with a large visible list of CVEs, related findings, and submission guidance.

Clear24/30
Useful24/30
Specific12/20
Complete12/20
Anthropic Credited CVEs screenshot

Why it was accepted

The page clearly describes an AI-adjacent security project with concrete evidence: it tracks Anthropic-credited vulnerabilities, shows a sizable CVE list, includes counts and contribution guidance, and presents enough visible content to be useful as a public listing.
Weakness

The crawl does not show how the list is sourced or verified, what the update process looks like, or whether the data can be exported or queried outside the repository.

Review status

12 days ago #2387 ↑ +1

Last evaluated 12 days ago. Current rank #2387. Up 1 spot in the rankings.

Score history

72

Related listings

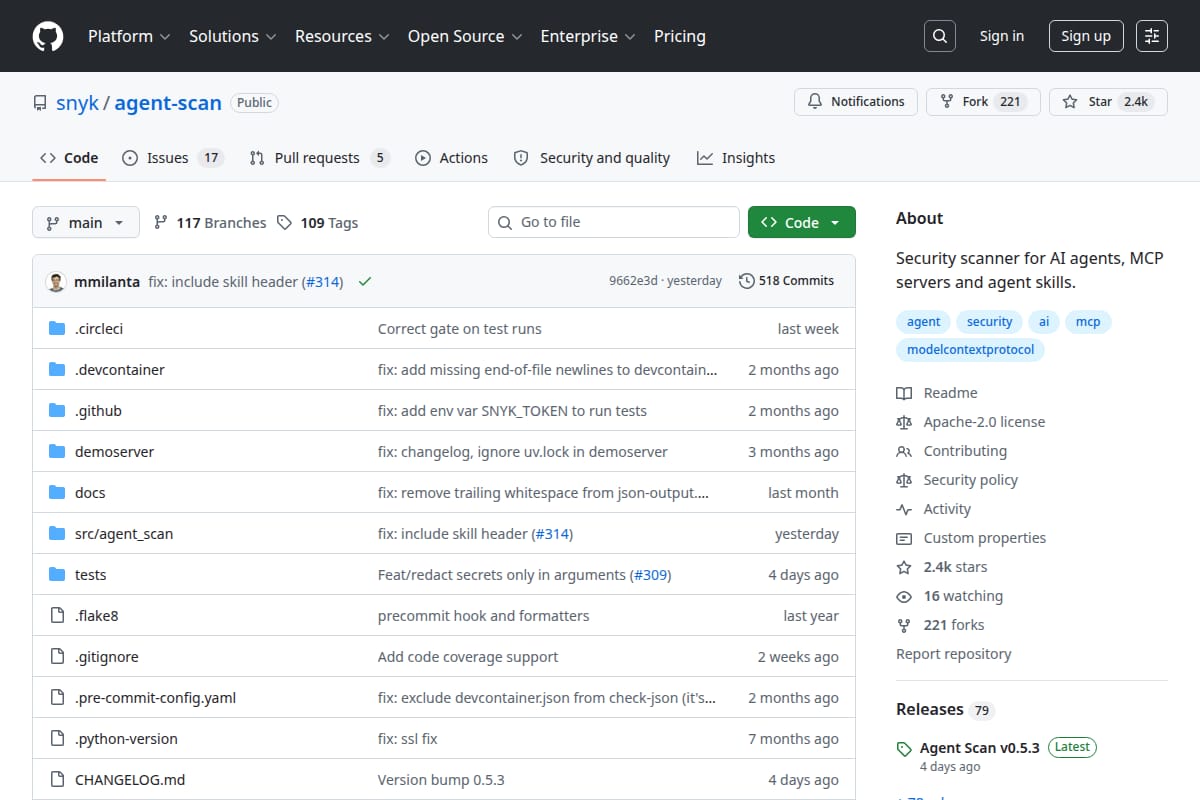
Snyk Agent Scan screenshot

Security / Agent Security

Open-source security scanner for AI agents, MCP servers, and agent skills. It auto-discovers installed agent components and checks them for prompt injection, tool poisoning, secrets, malware payloads, and related risks.

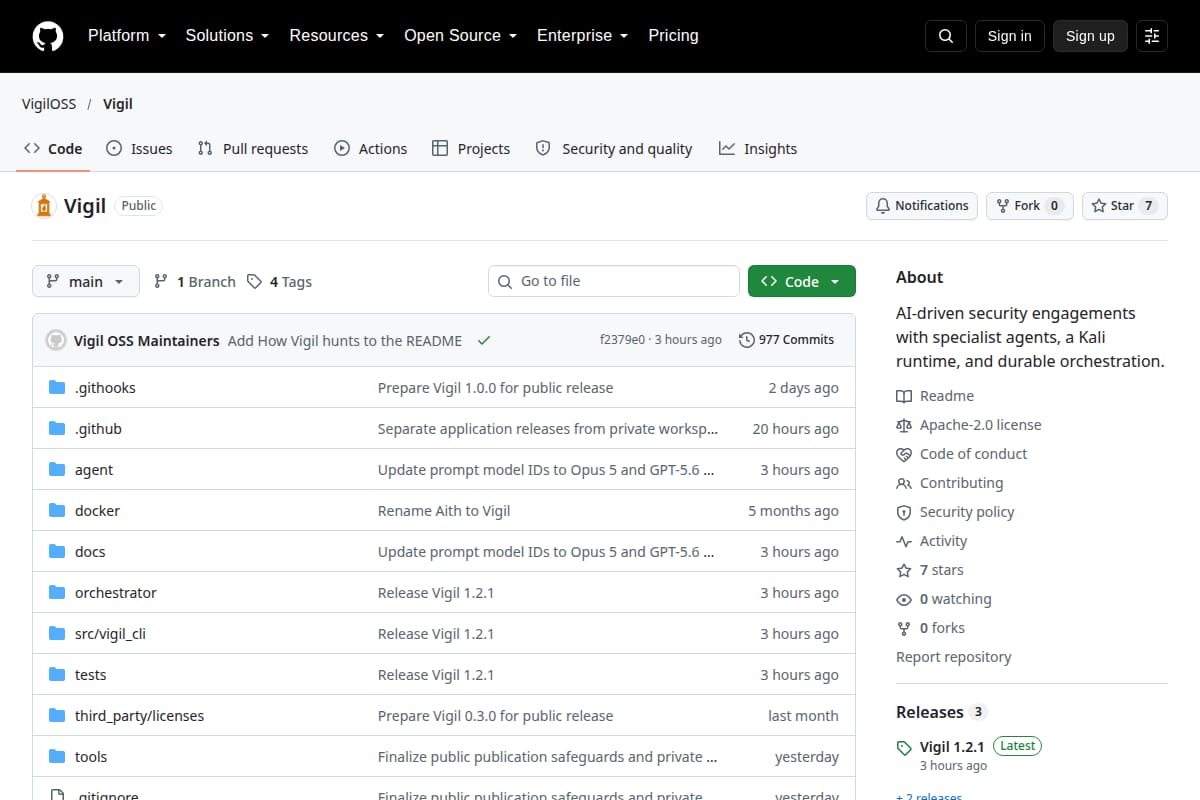
Vigil screenshot
#14 Vigil
91

Security / Penetration Testing

An AI harness for long-running penetration tests, bug bounties, and code audits. It combines specialist agents, a Kali runtime, durable state, and second-agent verification for findings.

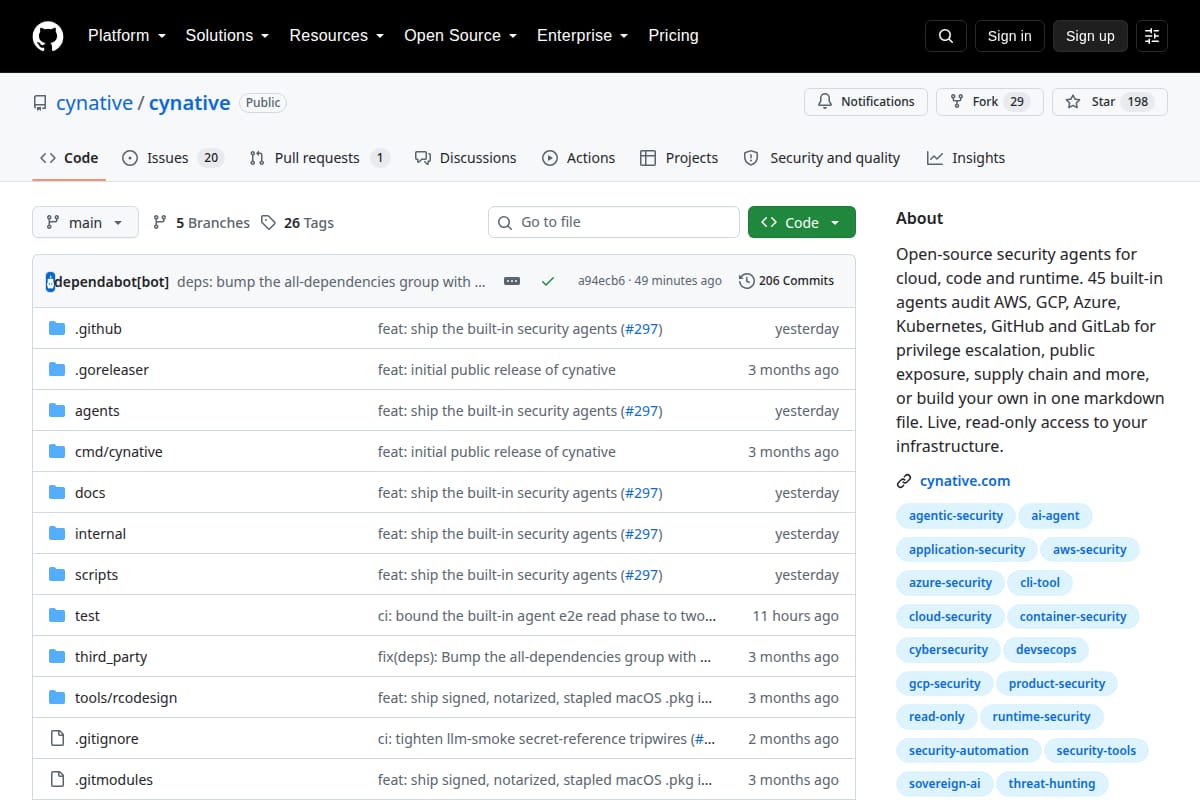
Cynative screenshot
#16 Cynative
91

Security / Cloud Security

Open-source security agent framework for cloud, code, and runtime. It ships 45 built-in agents for AWS, GCP, Azure, Kubernetes, GitHub, and GitLab, and lets users create custom agents in a single markdown file.

Xalgorix screenshot
#75 Xalgorix
90

Security / Penetration Testing

Self-hosted AI security testing platform for authorized pentesting and bug bounty workflows, with a local web UI, live agent telemetry, verified findings, and branded PDF reports.