
AgentDish directory
Security AI Tools
Accepted listings in this category.
| Listing | Category | Score | Trend | Checked | |
|---|---|---|---|---|---|
#12
↑ +16
Snyk Agent Scan
Open-source security scanner for AI agents, MCP servers, and agent skills. It auto-discovers installed agent components and checks them for prompt injection, tool poisoning, secrets, malware payloads, and related risks. |
Security / Agent Security | 92 | ↑ +16 | 162 days ago | Details |
#14
↓ -3
Vigil
An AI harness for long-running penetration tests, bug bounties, and code audits. It combines specialist agents, a Kali runtime, durable state, and second-agent verification for findings. |
Security / Penetration Testing | 91 | ↓ -3 | 5 days ago | Details |
#16
↓ -3
Cynative
Open-source security agent framework for cloud, code, and runtime. It ships 45 built-in agents for AWS, GCP, Azure, Kubernetes, GitHub, and GitLab, and lets users create custom agents in a single markdown file. |
Security / Cloud Security | 91 | ↓ -3 | 37 days ago | Details |

#75
↓ -2
Xalgorix
Self-hosted AI security testing platform for authorized pentesting and bug bounty workflows, with a local web UI, live agent telemetry, verified findings, and branded PDF reports. |
Security / Penetration Testing | 90 | ↓ -2 | 102 days ago | Details |
#192
→ 0
Bright Security Agent
GitHub Marketplace app from NeuraLegion that scans apps and APIs for vulnerabilities, proposes fixes, and validates remediations inside GitHub workflows. |
Security / Application Security | 89 | → 0 | 131 days ago | Details |

#248
↓ -3
geiger
A read-only CLI that inventories AI agents, MCP servers, plugins, and AI extensions on a machine and explains what each one can access. |
Security / AI Security | 88 | ↓ -3 | 37 days ago | Details |
#317
↓ -3
Belay
Belay is an open-source, local-first security layer for AI coding agents. It blocks dangerous commands, secret leaks, prompt injection, and risky MCP tool calls, with human approval flows and support for multiple agents. |
Security / AI Agent Security | 88 | ↓ -3 | 81 days ago | Details |
#498
↓ -4
OneCLI
Open-source credential gateway for AI agents that injects service credentials without exposing the real keys to the agent. Includes a vault, access tokens, host/path matching, and local quick-start instructions. |
Security / Secrets Management | 87 | ↓ -4 | 84 days ago | Details |
#590
↑ +2
MILLENNIUMS.AI / Redthread
AI-native application protection platform with autonomous LLM pentesting, proof-of-concept exploit findings, and a full API-driven workflow for scans, reporting, and remediation. |
Security / AI App Pentesting | 86 | ↑ +2 | 18 days ago | Details |
#739
↑ +2
Bulwark
Kernel-level read gate for AI coding agents that blocks protected file reads before bytes reach the agent, with Linux fanotify and macOS Endpoint Security support. |
Security / Developer Security Tool | 86 | ↑ +2 | 108 days ago | Details |
#892
↓ -3
Numbat
Open-source endpoint visibility and response for AI agents, with local detection, optional pre-action blocking, and forensic reconstruction. |
Security / Endpoint Security | 85 | ↓ -3 | 78 days ago | Details |
#898
↓ -3
LLM Red Team Lab
A hands-on kit for authorized red teaming of locally run LLMs, with jailbreak techniques, prompt-injection scenarios, streaming attack visualization, and support for OpenAI-compatible local model servers. |
Security / AI Red Teaming | 85 | ↓ -3 | 81 days ago | Details |
#930
↓ -3
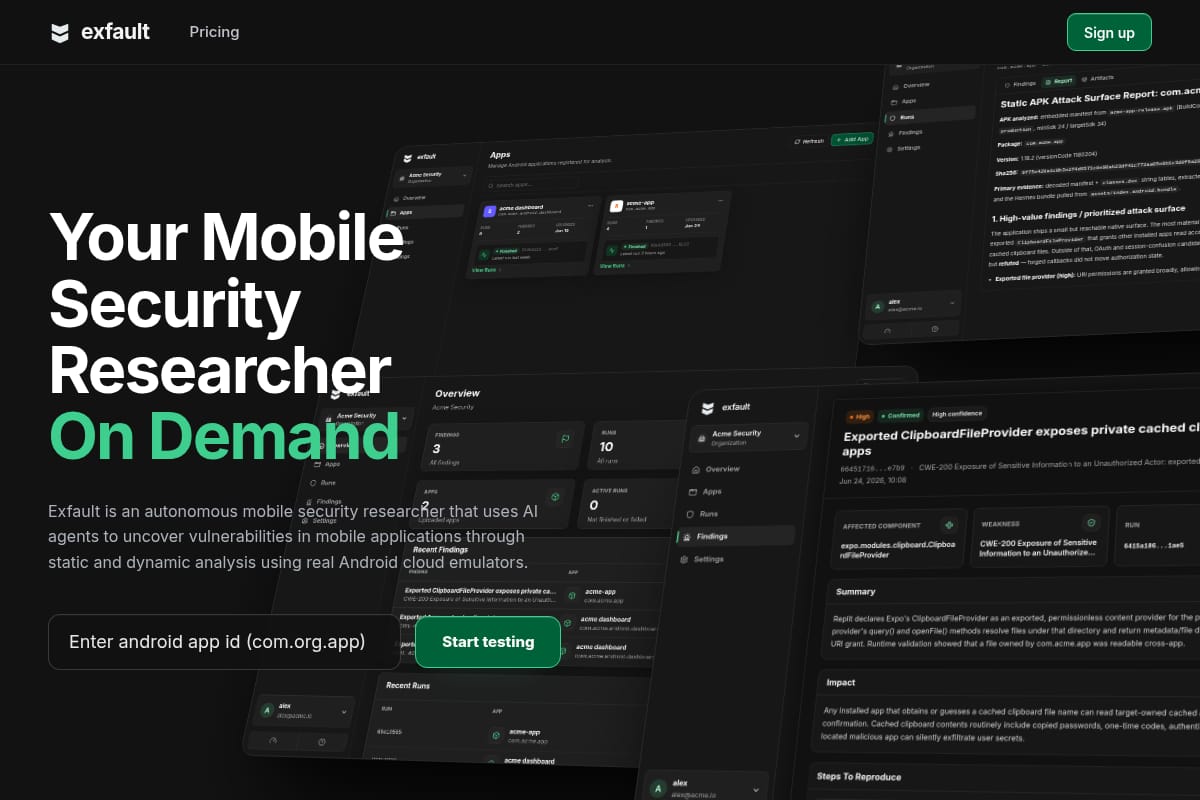
Exfault
Exfault is an autonomous Android security testing tool that uses AI agents, static analysis, dynamic analysis, authenticated workflows, and cloud emulators to produce reproducible findings and reports. |
Security / Mobile Security | 85 | ↓ -3 | 109 days ago | Details |
#960
↓ -3
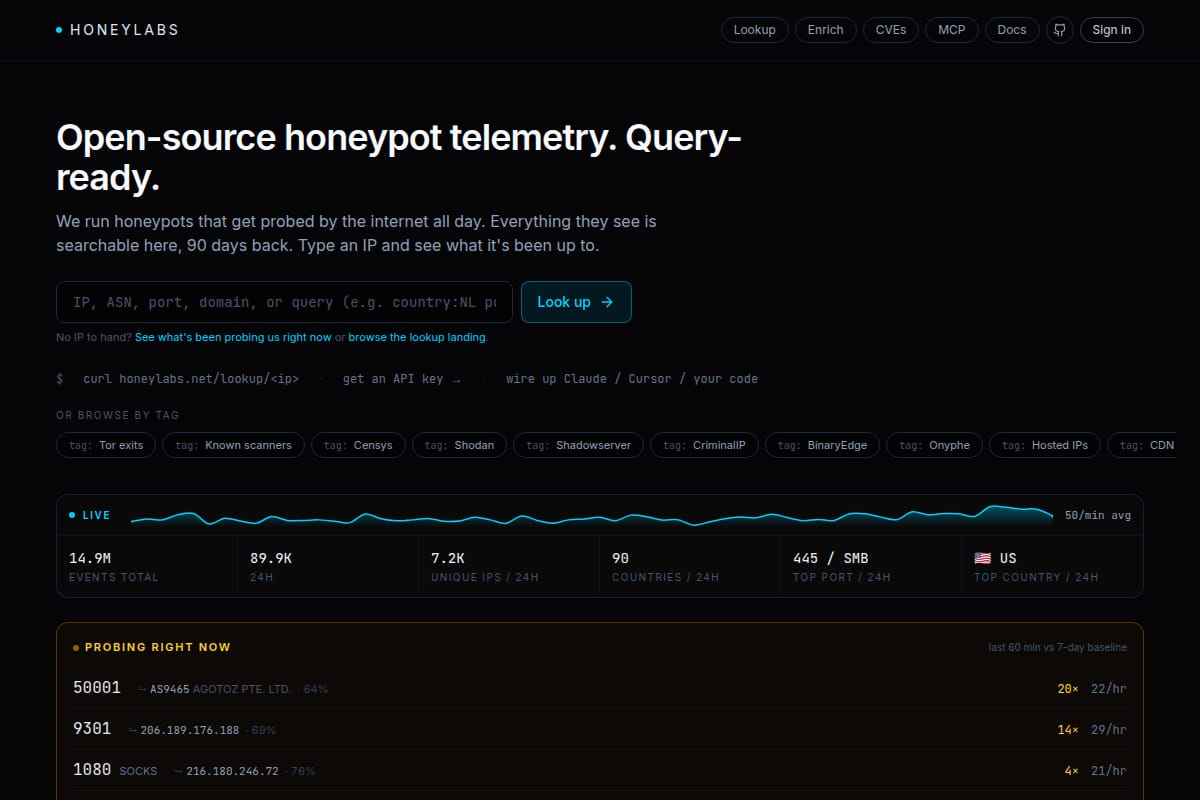
HoneyLabs
A honeypot telemetry and threat intelligence service with searchable IP lookups, recent scanner data, and an MCP/JSON-RPC API for agents and developers. |
Security / Threat Intelligence | 85 | ↓ -3 | 151 days ago | Details |
#990
↓ -6
Outis
A command-line tool that sends fake RFC 3464 bounce messages to make spam senders think an address does not exist. The README explains the workflow, configuration, batch mode, multiple-account handling, and provider-specific caveats. |
Security / Email Security | 84 | ↓ -6 | 13 days ago | Details |
#1148
↓ -6
ASL V6
Open-source security research tool for auditing Python AI agents and codebases with AST analysis and Docker-based runtime verification. |
Security / AI Security / Red Teaming | 84 | ↓ -6 | 81 days ago | Details |
#1163
↓ -6
Sunglasses
Open-source input scanner for AI agents that strips hidden instructions and scans text, files, images, PDFs, QR codes, audio, and video before they reach an agent. |
Security / AI Security / Prompt Injection Defense | 84 | ↓ -6 | 85 days ago | Details |

#1221
↓ -6
Declaw Arena
An interactive CTF-style challenge where users try to break or exfiltrate data from sandboxed AI agents running in Declaw’s isolated runtime. |
Security / AI Agent Security | 84 | ↓ -6 | 105 days ago | Details |
#1274
↓ -6
Defending Code Reference Harness
An open-source reference implementation for autonomous vulnerability discovery and remediation with Claude. It includes Claude Code skills for threat modeling, scanning, triage, patching, plus a harness for running a recon → find → verify → report → patch pipeline. |
Security / AI Security | 84 | ↓ -6 | 133 days ago | Details |
#1419
↓ -3
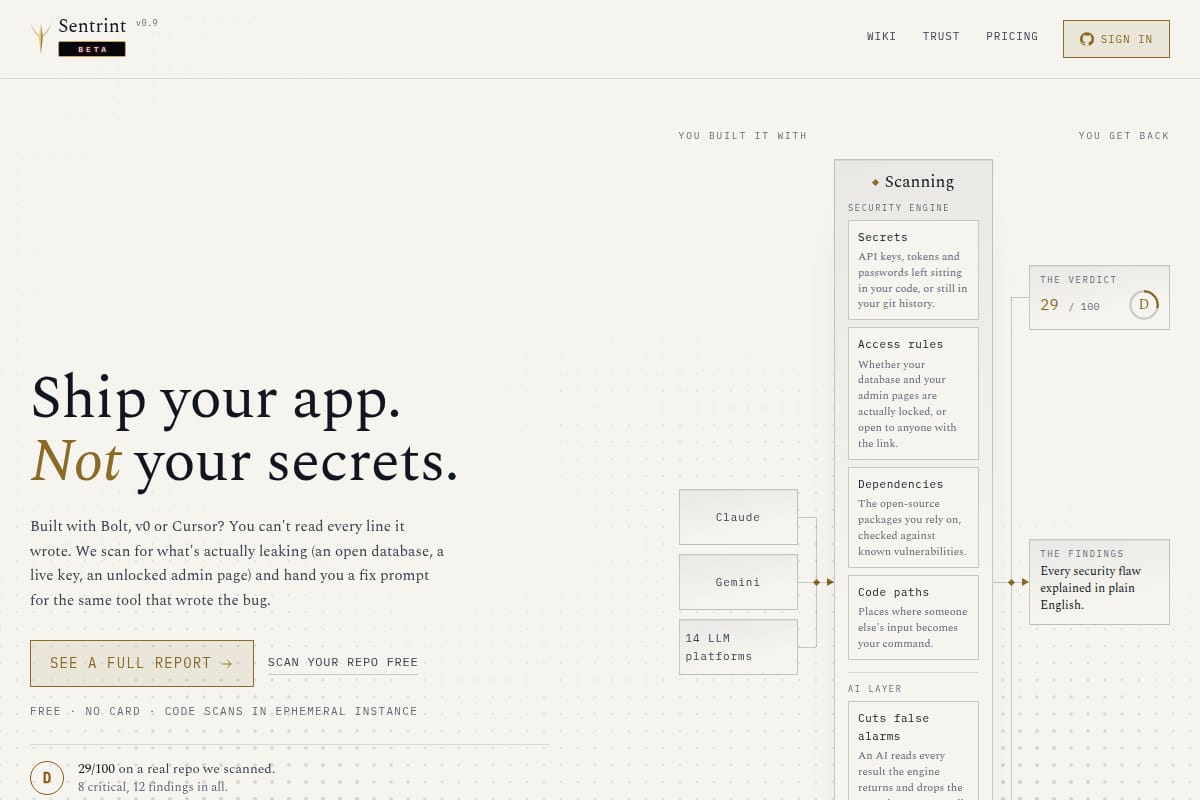
Sentrint
Sentrint is a security scanner for apps built with LLM platforms like Bolt, Cursor, and v0. It scans repos for secrets, access rules, vulnerable dependencies, and risky code paths, then returns plain-English findings and a copy-paste fix prompt. |
Security / Code Security | 83 | ↓ -3 | 57 days ago | Details |
#1566
↓ -2
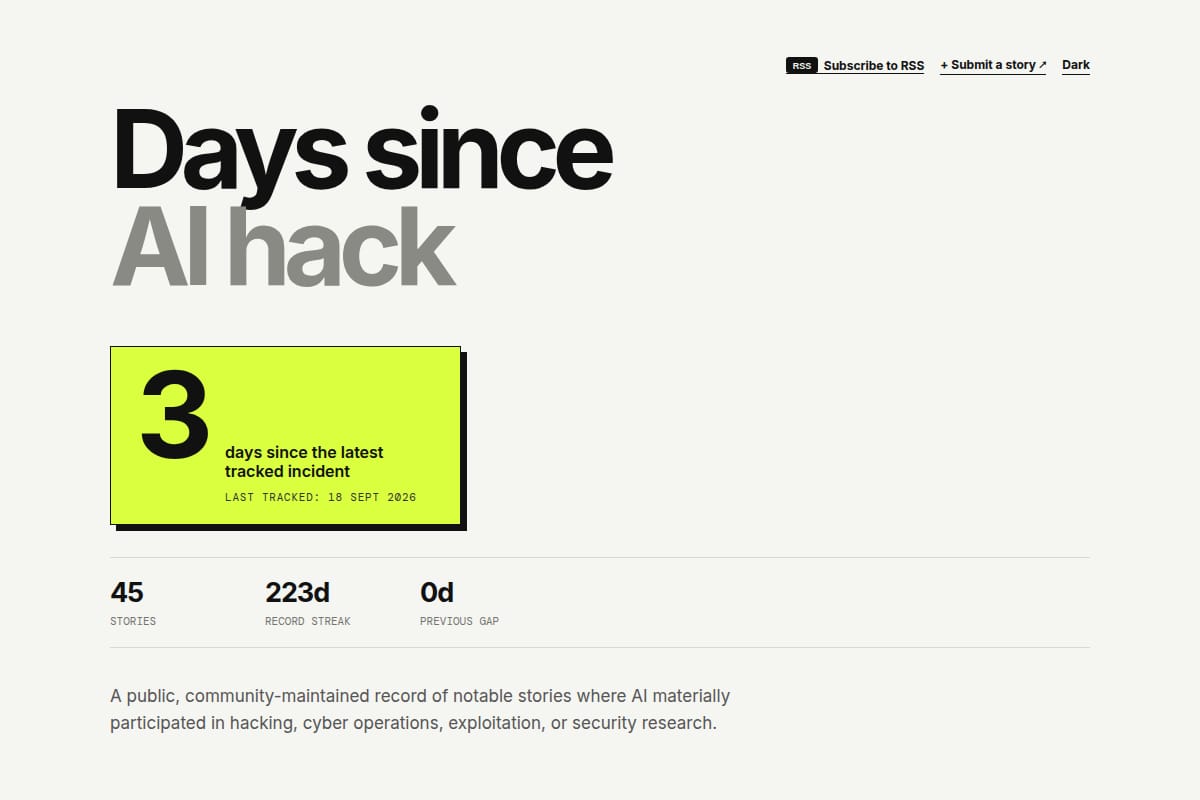
AI Hack Watch
A public timeline and dataset of notable AI-involved hacking and cyber incidents, with RSS support and source links for each entry. |
Security / AI Security Research | 82 | ↓ -2 | 25 days ago | Details |
#1644
↓ -2
PISIGuard
A browser extension that masks personal and sensitive information before you send messages to AI chat tools, then restores the original values in the reply. |
Security / Privacy | 82 | ↓ -2 | 74 days ago | Details |

A blog post describing Annex, a local-AI security tool that encrypts selected files during agent sessions to keep sensitive data away from local AI tools. The post explains the threat model, encryption flow, and the stack used to build it. |
Security / Local AI Security | 82 | ↓ -2 | 88 days ago | Details |

#1725
↓ -2
Blue41
Blue41 is an enterprise risk control platform for AI agents. The site says it monitors agent behavior in production, detects prompt-injection-style incidents and unauthorized activity, and helps teams control sensitive workflows and compliance risk. |
Security / AI Security | 82 | ↓ -2 | 127 days ago | Details |